← Daily Brief for September 30, 2026
OpenShell puts enforceable permissions outside the agent
Focus: Technical AI Engineering
Date: September 28, 2026
Topics: agent runtime, permissions, sandboxing, credential isolation, formal policy
Evidence: Official Primary Source
Availability: Published
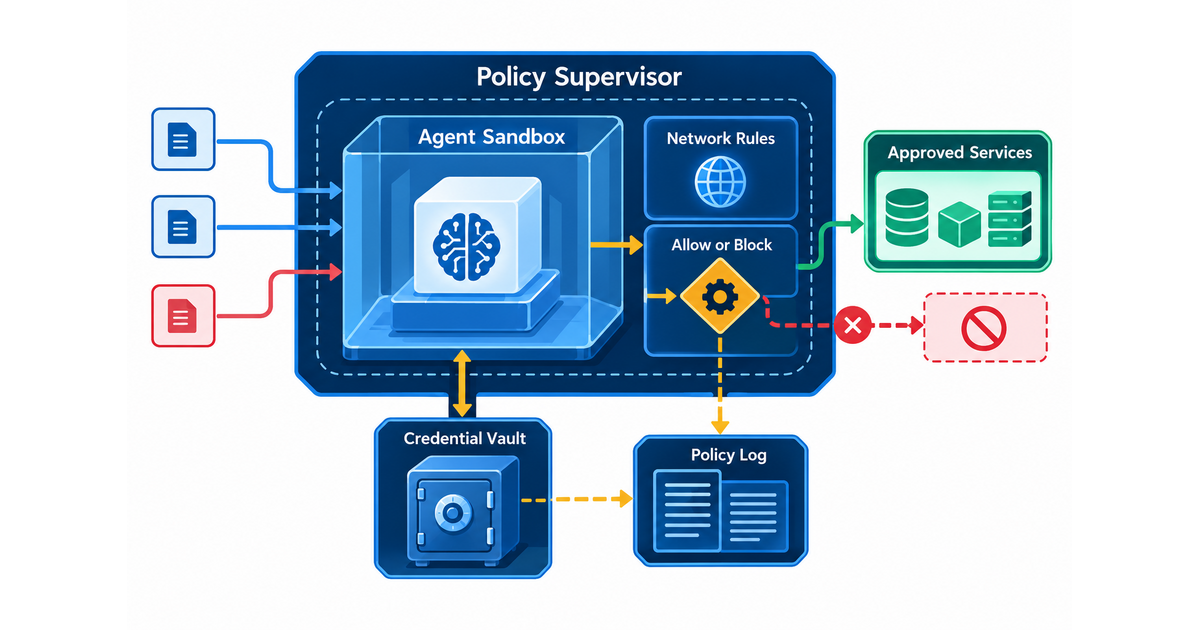
Summary: NVIDIA describes OpenShell 0.1.0 as an open-source runtime that can wrap existing agents with sandboxed execution, service controls, credential isolation, network policy, and formal policy analysis. Its examples show the runtime allowing read operations while blocking writes and keeping real credentials outside the agent workload.
Why it matters: Long-running agents become more useful as they gain access to files, services, credentials, and production systems, but that also raises the cost of mistakes. External runtime controls give engineering teams a way to constrain what an agent can actually do without relying on the agent to police itself.
What to do now
Put one existing agent behind deny-by-default runtime controls: Choose a bounded coding or operations workflow, allow only the services and actions it needs, log every denial, and review whether the policy blocks unsafe actions without preventing legitimate work.
Source: OpenShell puts enforceable permissions outside the agent