← Daily Brief for September 22, 2026
Benchling treats agent-generated code as untrusted in a multi-tenant security design
Focus: Agents for Everyone
Date: September 21, 2026
Topics: agent security, sandboxing, multi-tenancy, data exfiltration
Evidence: Official Announcement
Availability: Published
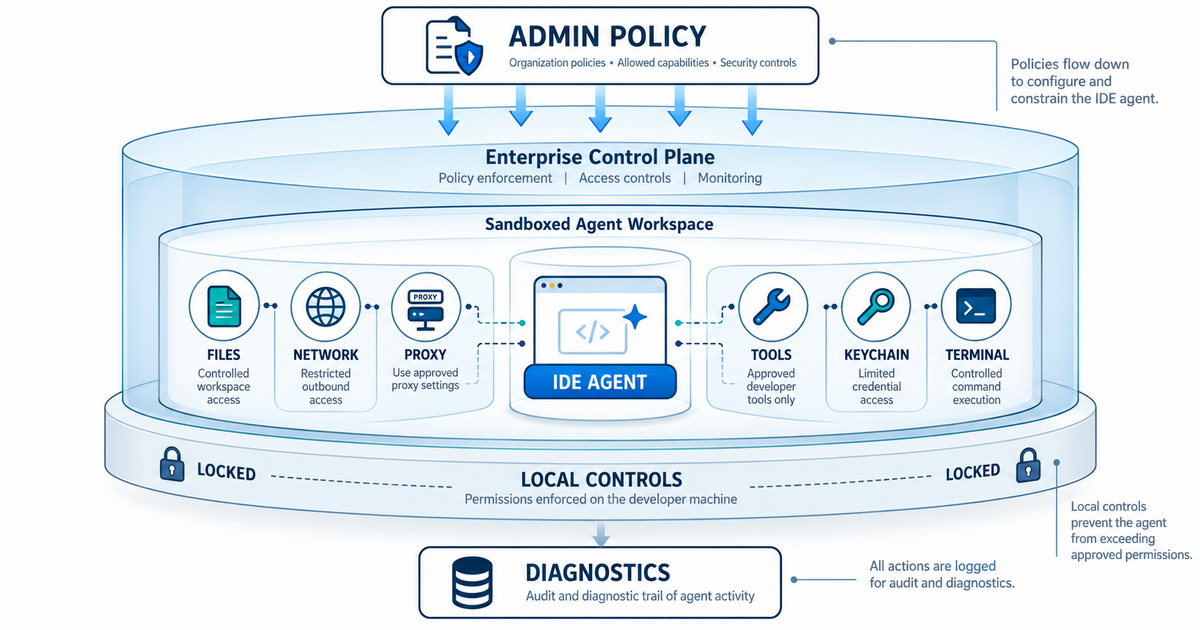
Summary: AWS describes how Benchling runs AI agent-generated scientific code using AgentCore Code Interpreter in VPC mode, combining network isolation, DNS controls, and endpoint policies to reduce cross-tenant and data-exfiltration risk.
Why it matters: As agents gain the ability to write and run code, the key design assumption should be that generated code is untrusted. Security has to come from containment, least privilege, network controls, tenancy boundaries, and observable execution—not confidence in the model.
What to do now
Treat agent code as untrusted: Place code-executing agents behind isolated runtimes, least-privilege policies, outbound network controls, tenant boundaries, and audit logs.
Source: How Benchling secured multi-tenant AI agents with Amazon Bedrock AgentCore