← Daily Brief for September 16, 2026
Google moves agent security from syntax checks to runtime intent controls
Focus: Technical AI Engineering
Date: September 15, 2026
Topics: agent security, runtime governance, semantic policy, anomaly detection
Evidence: Official Documentation
Availability: General Availability
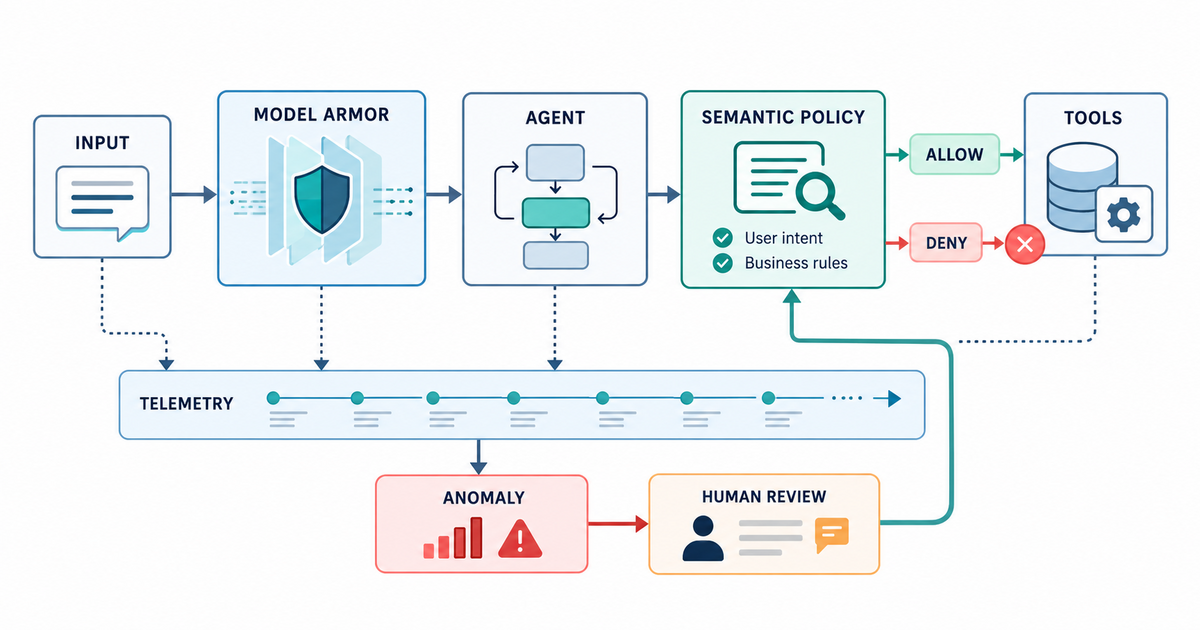
Summary: Google published a reference architecture for moving agent safeguards outside application code and into the Gemini Enterprise Agent Platform. Agent Gateway combines Model Armor at ingress and egress, natural-language Semantic Governance Policies before tool execution, and Agent Anomaly Detection across sessions; the companion repository includes local simulators and deterministic tests.
Why it matters: The design separates payload screening, intent authorization and multi-turn behavior monitoring instead of treating prompt injection as the only failure mode. Google’s examples and detector confidence values are explicitly illustrative, so teams still need their own threat models, policy tests, false-positive review and human escalation paths before production use.
What to do now
Threat-model one tool action: Choose one irreversible tool call, then specify ingress screening, intent policy, session anomaly signals and a human escalation before testing the reference pattern.
Source: Build zero-trust AI agents that judge intent, not just syntax