← Daily Brief for September 16, 2026
Cloudflare scopes teammate, CI, and agent access to individual Workers
Focus: Technical AI Engineering
Date: September 15, 2026
Topics: least privilege, agent deployment, CI security, serverless governance
Evidence: Official Announcement
Availability: General Availability
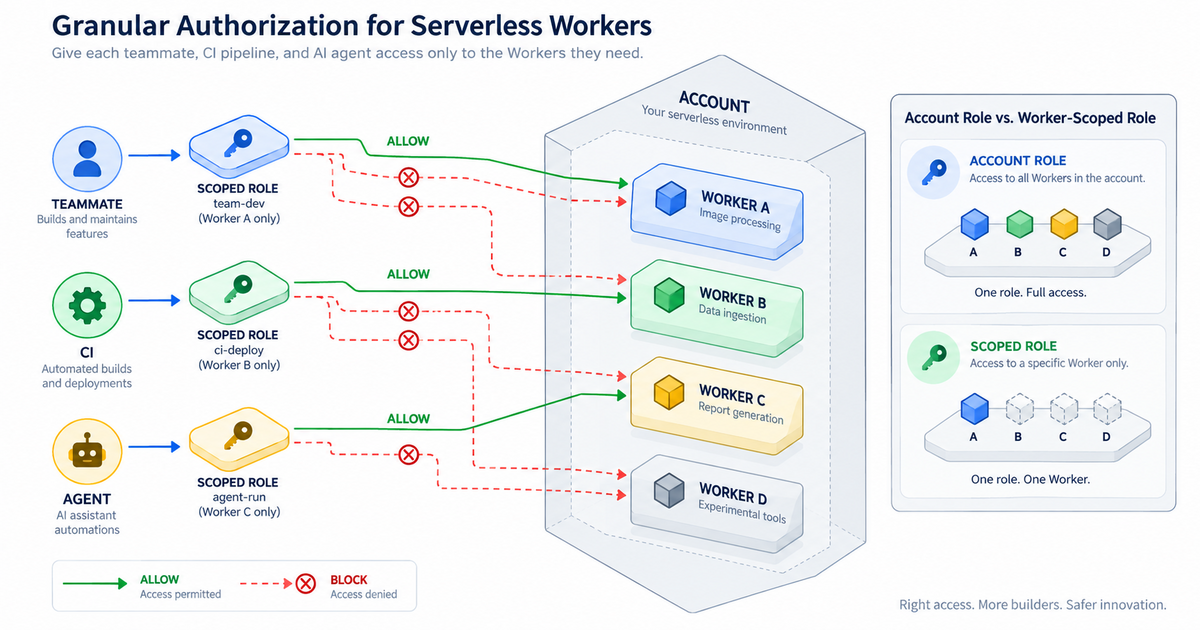
Summary: Cloudflare introduced Worker-scoped authorization so account owners can grant a teammate, CI system or AI agent access to specific Workers instead of the whole account. The model separates account-wide and Worker-scoped roles and supports narrower build, deploy and management paths.
Why it matters: Deployment agents are safer when their credentials cannot reach unrelated applications. This reduces blast radius and makes separation of duties easier to audit, but least privilege still depends on correct role design, token handling, logs and periodic access review; scoped authorization does not validate the code an agent deploys.
What to do now
Narrow one deployment credential: Inventory the Workers reachable by one CI or agent token, then replace account-wide access with the smallest Worker-scoped role that still completes the job.
Source: Give every teammate and agent the right level of access to your Workers