← Daily Brief for October 22, 2026
CrowdStrike documents threat actors experimenting with agentic attack workflows
Focus: Technical AI Engineering
Date: October 21, 2026
Topics: Agentic threats, Tool permissions, Attack harnesses
Evidence: Publisher Authored
Availability: Available
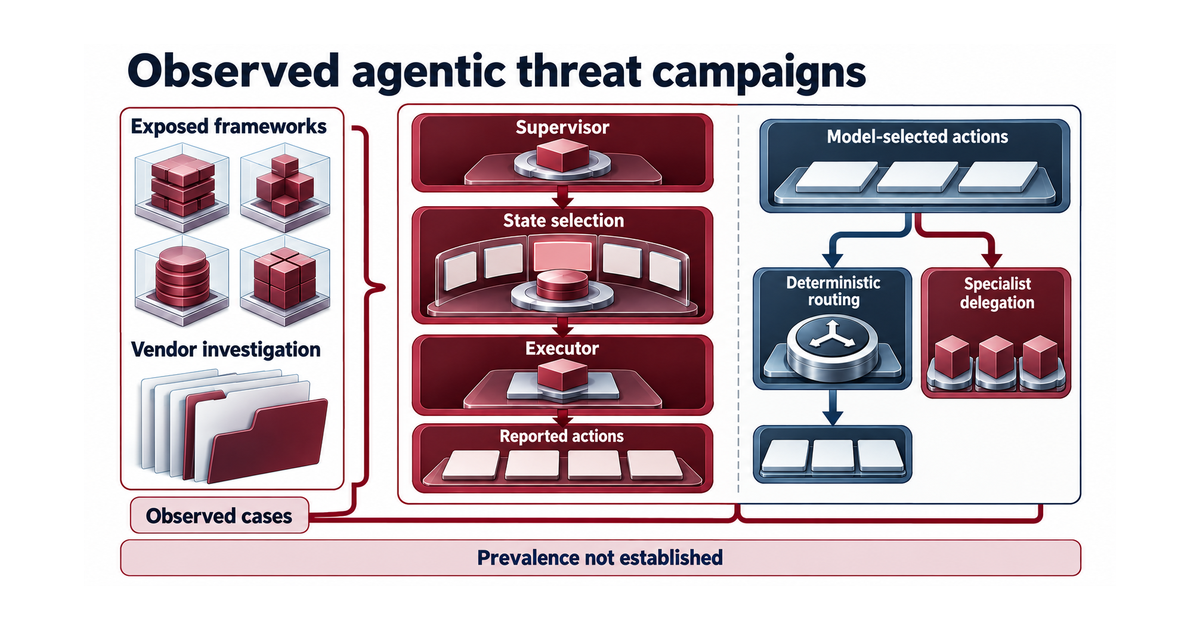
Summary: CrowdStrike describes four newly observed threat actors using exposed agent frameworks for reconnaissance and offensive workflows. The campaigns combined deterministic steps with model-selected actions or specialist agents, according to the vendor’s incident analysis. The evidence shows concrete attacker experimentation, but it comes from one security company and does not establish prevalence.
Why it matters: Security teams can inventory exposed agent interfaces, restrict tool permissions and log every action before testing detection rules against the described patterns. The practical lesson is to evaluate an agent’s surrounding harness and access paths, not only its language model.
Source: CrowdStrike Uncovers New Agentic AI Campaigns