← Daily Brief for October 16, 2026
Agentic autofix couples security repairs with a fresh CodeQL check
Focus: Technical AI Engineering
Date: October 15, 2026
Topics: Security repair loops, CodeQL validation, Draft pull requests
Evidence: Publisher Authored
Availability: Available
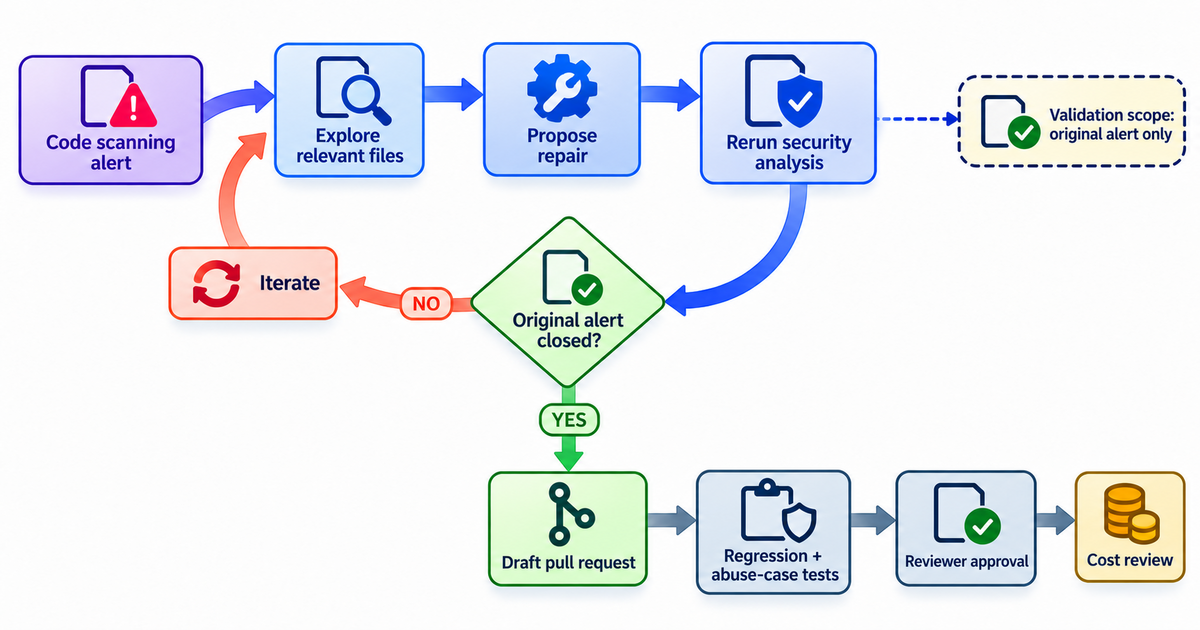
Summary: GitHub's agentic autofix now explores relevant repository files, proposes a repair, reruns CodeQL, and iterates before opening a draft pull request. Teams may assign one alert or batch up to twenty-five default-branch alerts. The validation confirms that CodeQL closes the original alert, not that the patch preserves every behavior or removes unrelated risks.
Why it matters: Treat the generated pull request as evidence to review, not a finished remediation. Run regression and abuse-case tests, inspect permission and dependency changes, confirm the alert's root cause, and track AI-credit and Actions-minute costs before scaling.
Source: Agentic autofix for code scanning alerts general availability