← Daily Brief for October 16, 2026
GitHub's AI Scan adds advisory vulnerability findings to pull requests
Focus: Technical AI Engineering
Date: October 15, 2026
Topics: Advisory security scans, Pull request review, CodeQL coverage
Evidence: Publisher Authored
Availability: Available
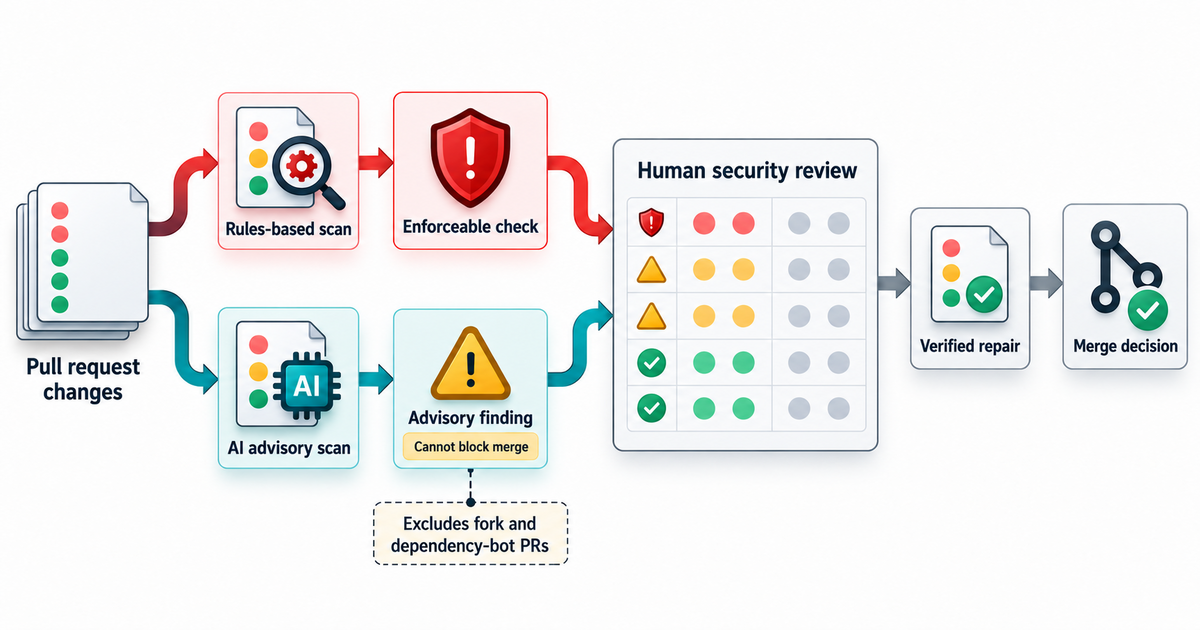
Summary: GitHub made AI Scan generally available for pull requests, adding model-generated security findings beside CodeQL results for languages and frameworks outside current CodeQL coverage. Findings can explain risk and suggest a repair, but they remain advisory: they cannot fail the check, block merges, inspect forked contributions, or scan Dependabot pull requests.
Why it matters: Security teams should measure precision, missed defects and reviewer workload before treating AI Scan as a control. Keep enforceable CodeQL and ruleset gates, label AI findings clearly, and require human verification of every suggested fix before merging.
Source: AI Scan for pull requests generally available