← Daily Brief for October 15, 2026
Workflow lockfiles give agent CI a reproducible dependency boundary
Focus: Technical AI Engineering
Date: October 14, 2026
Topics: Dependency provenance, Workflow security, Reproducible CI
Evidence: Publisher Authored
Availability: Available
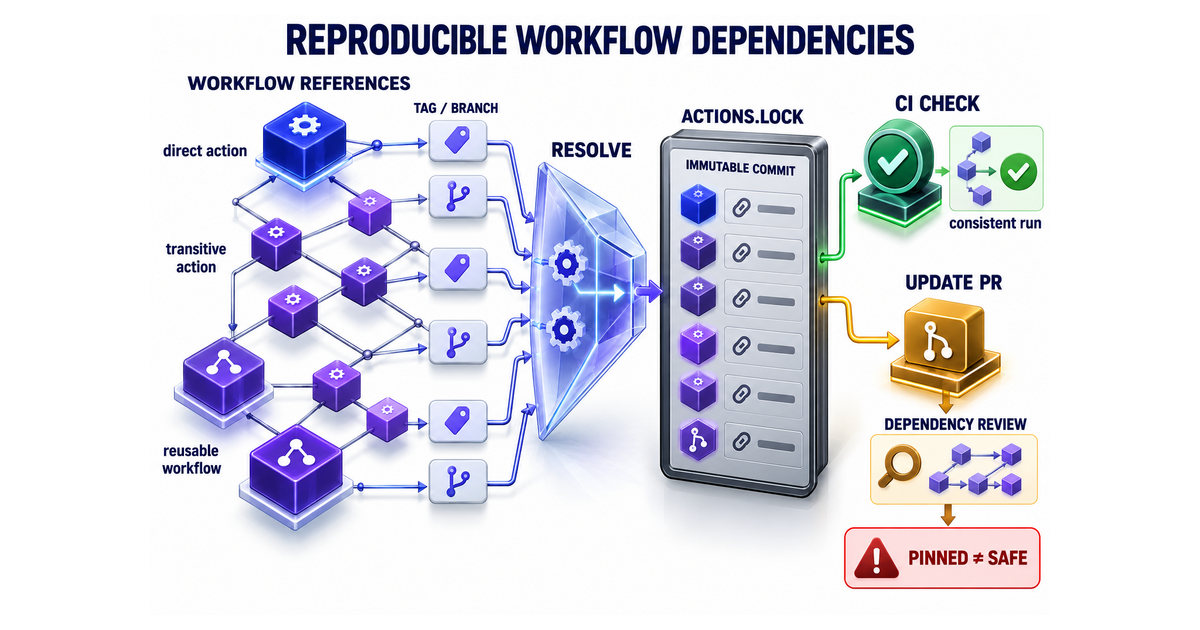
Summary: GitHub introduced public-preview workflow lockfiles that record immutable commit identifiers for Actions dependencies, including reusable workflows. Its gh actions-lock extension can create and check the lockfile, and Dependabot can update pinned entries through reviewable pull requests. For AI-generated code and agent-driven automation, the mechanism narrows unreviewed dependency drift but does not certify that pinned code is safe.
Why it matters: Ask agents to propose dependency upgrades rather than silently changing action versions. Review pinned code and permissions, test the resulting workflow, and require lockfile consistency in continuous integration. Reproducibility helps incident analysis but cannot replace supplier security assessment.
Source: GitHub Actions workflow lockfiles in public preview