Copilot local sandboxing makes agent tool permissions an OS-level boundary
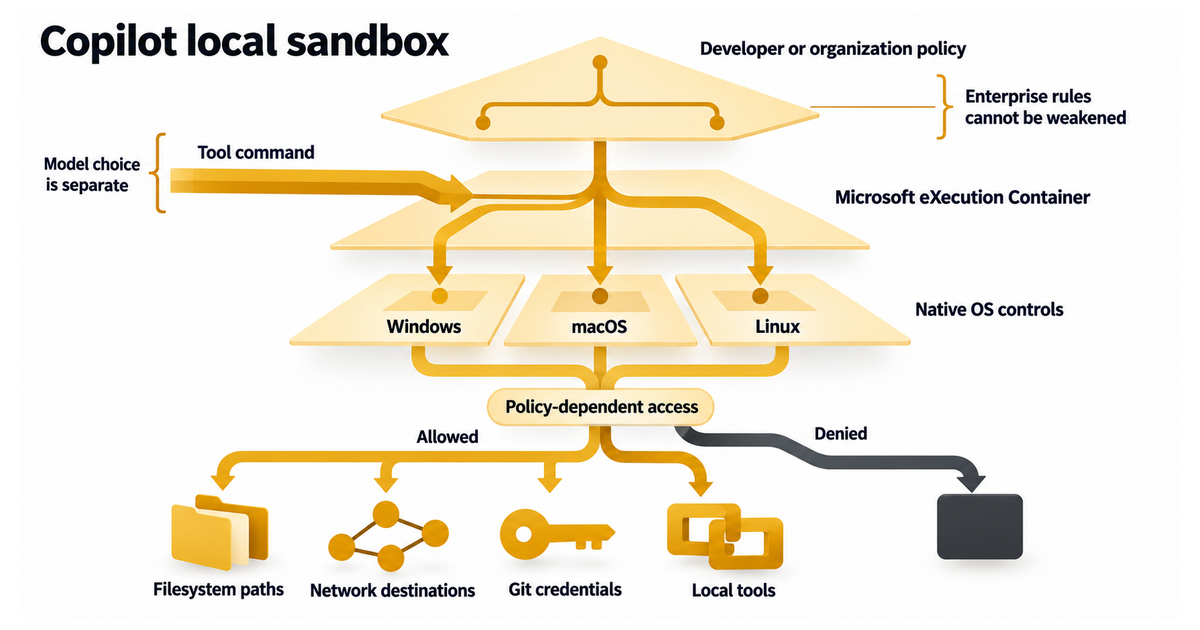
GitHub says local sandboxing is now generally available in Copilot CLI, the GitHub Copilot application, and VS Code Agent Host sessions. The mechanism places a developer- or administrator-defined access policy between agent-generated tool commands and the resources those commands would touch. Filesystem paths, internet and local-network destinations, Git credentials, and selected tools can be allowed or denied. Microsoft eXecution Container translates the shared policy into native operating-system enforcement on Windows, macOS, and Linux. Enterprise-managed settings can require sandboxing and prevent an individual developer from weakening the rules. The key architectural distinction is that restricting tool execution is independent of which language model produces the tool call: a capable model still runs inside the same boundary. A sandbox does not mean every output is correct, and policy quality still matters. This is a local execution protection, not evidence that every remote cloud-agent or third-party integration is automatically covered.
Copilot local sandboxing makes agent tool permissions an OS-level boundary
Focus: Technical AI Engineering Date: October 7, 2026 Topics: agent security, sandbox policy, tool execution, filesystem and network permissions Evidence: Publisher Authored Availability: Available
Summary: GitHub says local sandboxing is now generally available in Copilot CLI, the GitHub Copilot application, and VS Code Agent Host sessions. The mechanism places a developer- or administrator-defined access policy between agent-generated tool commands and the resources those commands would touch. Filesystem paths, internet and local-network destinations, Git credentials, and selected tools can be allowed or denied. Microsoft eXecution Container translates the shared policy into native operating-system enforcement on Windows, macOS, and Linux. Enterprise-managed settings can require sandboxing and prevent an individual developer from weakening the rules. The key architectural distinction is that restricting tool execution is independent of which language model produces the tool call: a capable model still runs inside the same boundary. A sandbox does not mean every output is correct, and policy quality still matters. This is a local execution protection, not evidence that every remote cloud-agent or third-party integration is automatically covered.
Why it matters: As coding assistants execute real commands, a prompt instruction alone is not a credible access-control boundary. Teams can start by enumerating writable project folders, credential access, allowed network destinations and MCP tools, then test deliberate denied operations. Pair this containment with read-only execution auditing and quality review rather than treating sandbox enforcement as a complete safety system.